Security risk assessment & audit (SRAA)
Identify website risks and prioritise actionable fixes.
For companies assessing website security risks: get evidence-based findings, repair priorities and retest arrangements.
- Agree scope and authorisation
- Findings with evidence and priorities
- Arrange re-testing after fixes
PURPOSE & VALUE / AT A GLANCE
Understand the risks and which fixes come first.
A security review is needed, but the risks and improvement priorities are unclear.
Scope assets and permissions, assess risks and document evidence and fixes.
Owners can prioritise improvements and verify the fixes.
IN PRACTICE / SEE THE RESULT
See what goes in, and what you get back.
Choose a situation close to your needs.
Your information or need
Authorised website and system scope Important data, accounts and operations
Security risk assessment & audit (SRAA)
Review configuration, permissions and application risks and organise findings, evidence and recommendations.
Illustrative result
Risk and evidence explanations Prioritised repair recommendations
How this helps: Help owners decide what to fix first and who should handle it.
These examples illustrate use and delivery, rather than actual product screens or client results. Content, connections and deliverables depend on the agreed version and scope.
 USE SCENARIO
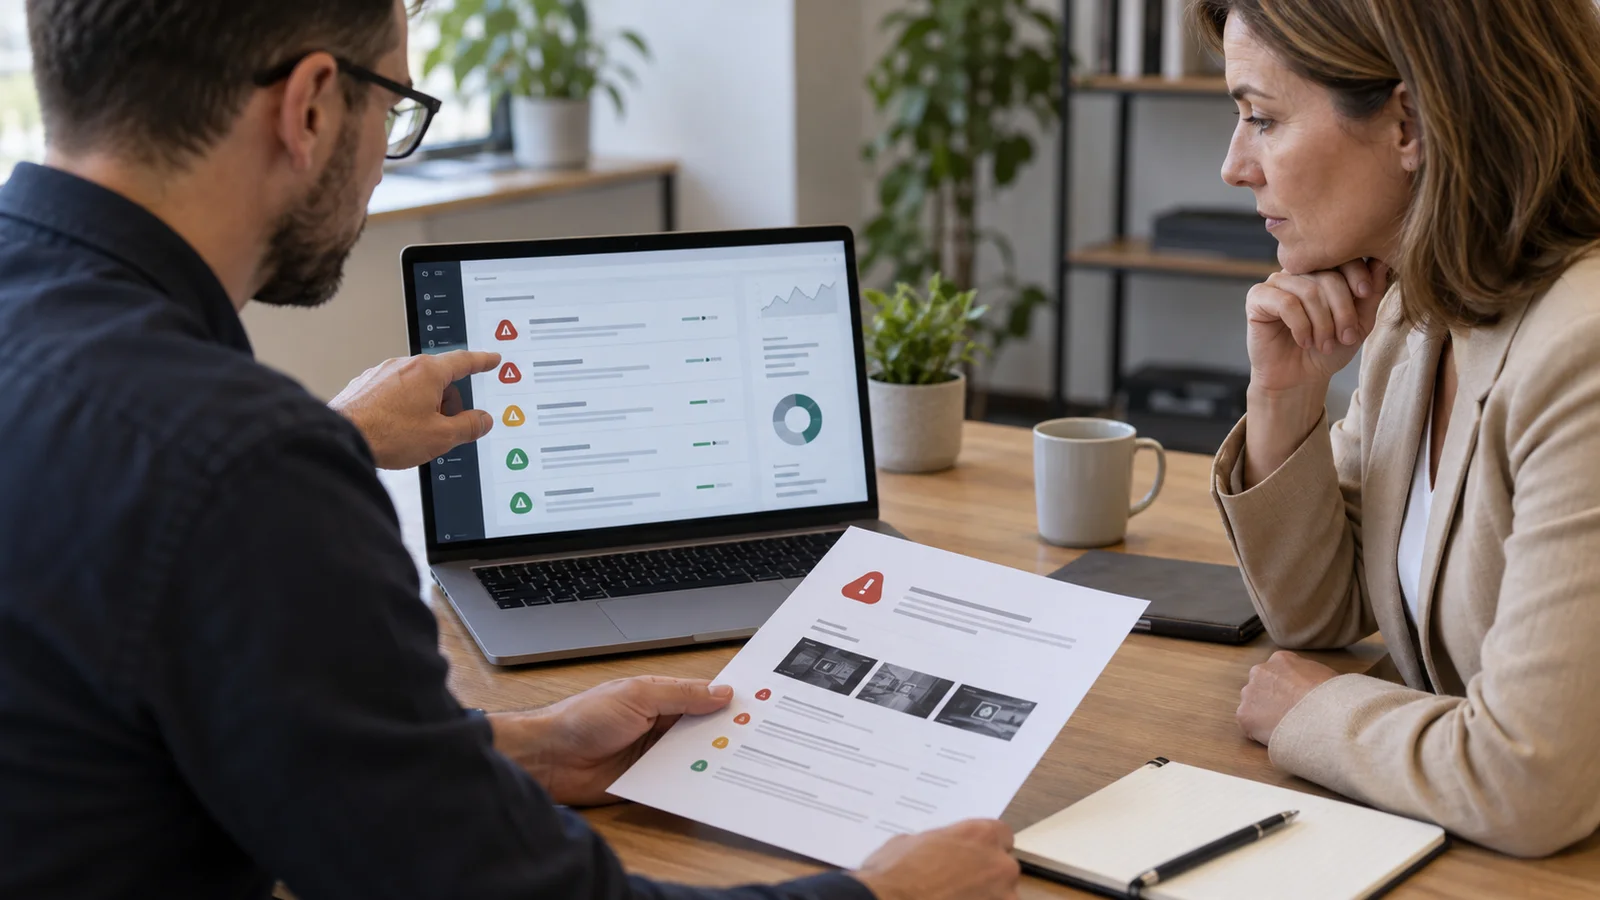
Prioritising fixes with the responsible team
For example, share findings and evidence with the website owner, prioritise settings or permission issues and arrange re-testing.
How it fits your work
- 01
Agree review scope
Review sites, data, permissions and boundaries.
- 02
Assess and document findings
Check settings and controls under authorisation.
- 03
Recommend fixes and re-test
Prioritise fixes and verify results.
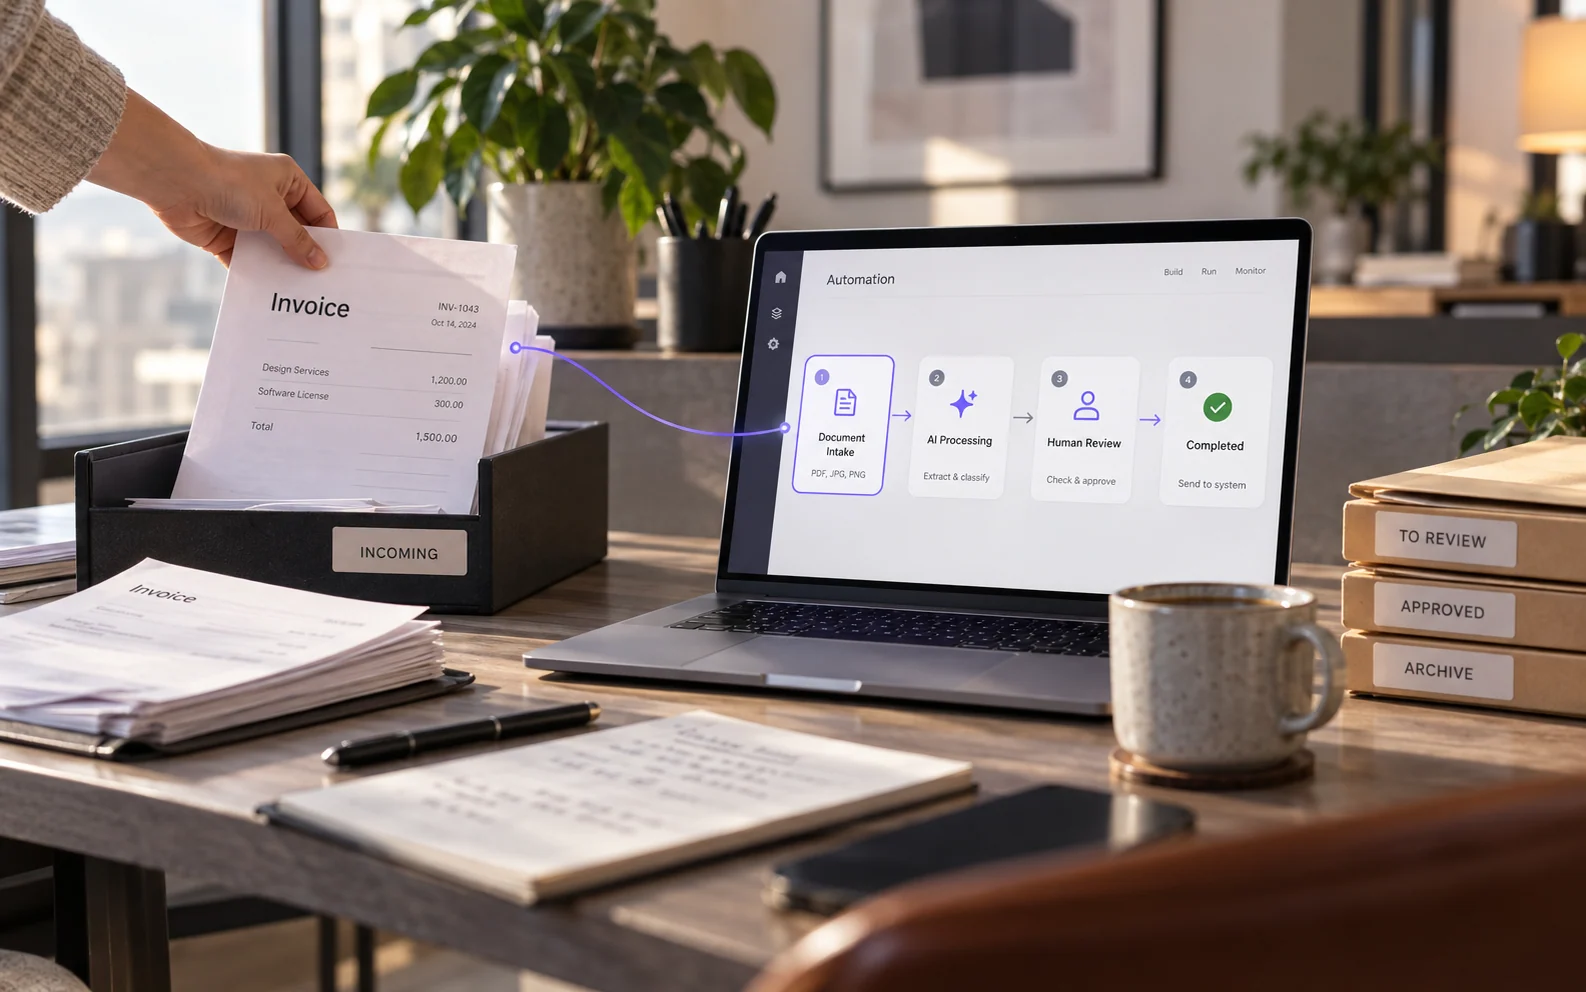
This AI-generated use scene is illustrative. Interfaces are not actual product screens or customer installations. Features and delivery depend on the agreed version and scope.
What the service covers
A clear scope and outcome, shaped around the way your business works.
Scope & risk
Inventory assets, data and system boundaries.
Technical & control review
Authorised checks of settings, permissions and app risks.
Prioritised fixes
Findings and evidence with actionable recommendations.
Re-test & follow-up
Verify fixes and record residual risk.
Teams and work it suits
- Systems handling customer data
- Organisations with audit or procurement requirements
Scope & risk
Technical & control review
Prioritised fixes
Bring the pieces together with a clear scope and outcome.
What to confirm before starting.
You don’t have to change everything at once. Understand the need, then decide on the next step together.
Understand & scope
Review your goals, current environment and delivery needs, then agree the scope.
Plan & deliver
Agree the approach and schedule, deliver the work and review progress together.
Verify & hand over
Check the outcome, prepare guidance and agree ongoing support.
Questions and getting started
What must be agreed before the assessment?
Agree assets, scope, authorisation, environments and timing, plus report content, contacts and required cooperation.
What will we receive afterwards?
Receive findings, evidence, risks and prioritised recommendations under the scope. Re-test as arranged and record remaining risks.
Can I get started now?
This solution is available on request. We’ll confirm the scope, cost and arrangements for your environment and needs before proceeding.